Privacy policy page SEO is the discipline of turning the legal page everyone ignores into a page that earns trust, impressions, and the occasional signup. I know how that sounds. A privacy page ranks for “privacy policy” and almost nothing else, right?
Not quite. In my experience auditing dozens of sites, the privacy page is the most under-optimized asset on the domain — and it quietly leaks authority every single day.
So here’s the deal. This isn’t a piece about hiding legal text in a footer and hoping nobody clicks. It’s a working privacy policy page SEO guide built around seven tips I’ve applied on real sites, with the numbers, the mistakes, and the messy parts included.
Grab a coffee. We’re going to make that dusty footer link pull its weight.
Why Privacy Policy Page SEO Matters More Than You Think
Most people treat the privacy page as a compliance chore. Focusing on privacy policy page SEO provides clear direction here. Write it once, paste it into the footer, forget it. That mindset is exactly why the page has so much untapped potential.
It sits on your root domain, inherits your site’s authority, and absorbs internal link equity from every page that carries a footer link.
Think about what the Privacy policy page SEO means in practice. On a typical WordPress build, the privacy page receives a footer link on every single URL. A thousand-page site hands that page a thousand internal links. No other page on your domain gets that treatment. That’s an enormous structural advantage most site owners never notice.
Then there’s the trust layer. Refining each detail of your privacy policy page SEO strengthens this section. Privacy is a real search intent now. People search for “[brand] privacy policy” before they hand over an email, a credit card, or a work account.
When that page loads fast, reads clearly, and answers the obvious questions, the visitor converts. When it’s a wall of legalese with a broken layout, they bounce and buy elsewhere.
The Three Audiences You are Actually Writing For
Before touching a single meta tag, map out who lands on the Privacy policy page SEO page. There are three groups, and they want very different things.
The first is the compliance visitor — the person checking whether the privacy policy page SEO sell data. They scan for specific phrases, find them, and leave. Fast scanning is their whole behavior pattern, so structure beats prose.
The second is the regulator or auditor. Effective execution in your Privacy policy page SEO makes a tangible difference. Less common, far higher stakes. They care about accuracy, dates, and whether the policy matches actual data practices. Any contradiction between your privacy page and your cookie banner is a real problem.
The third is the search engine itself. Crawlers parse the page, index the text, and evaluate whether it satisfies the query. That third audience is where privacy policy page SEO best practices actually live, and it’s the one most sites ignore completely.
Once the privacy policy page SEO see those three groups clearly, the rest of the work becomes obvious. Write for the scanner, protect the auditor, and structure for the crawler.
| Audience | Primary Goal | What They Scan For | How SEO Helps |
|---|---|---|---|
| Compliance visitor | Confirm data handling | Data sharing, retention, opt-out | Clear headings, jump links |
| Auditor or regulator | Verify accuracy | Effective date, contact, jurisdiction | Schema markup, consistent dates |
| Search engine | Match query intent | Topical relevance, structure | Titles, meta description, internal links |
| Prospect or buyer | Decide whether to trust you | Plain language, tone, transparency | Readability, fast load, mobile layout |
Tip 1: Give the Page a Real Title Tag, Meta Description, and URL Slug
The first privacy policy page SEO tip is embarrassingly simple, and it’s the one I see skipped most often. Most privacy pages ship with a title tag like “Privacy Policy — Company Name” and nothing else. No differentiation, no intent match, no reason to click.
That’s a wasted opportunity. Maintaining clarity across your Privacy policy page SEO remains essential. Your title tag is the single strongest on-page signal you control. Craft it so it does two jobs at once: identify the page and signal the value inside.
How to Write a Title Tag That Earns the Click
Keep the privacy policy page SEO under 60 characters so it doesn’t truncate in the SERP. Lead with the concept, not the brand. Something like “Privacy Policy | How We Handle Your Data” beats “Acme Corp Privacy Policy Statement Page” every time.
Add one concrete benefit or clarification. A thoughtful approach to Privacy policy page SEO reinforces your qualifications. “What We Collect and Why” works because it answers the question the visitor arrived with. Avoid vague filler like “Your Trust Matters To Us.” That phrase appears on maybe half a million pages and signals nothing.
Your meta description has the same job but with more room. Structuring your privacy policy page SEO around proven patterns ensures impact. Write it as a single sentence that states what the page covers and why it’s worth reading. Don’t waste the slot on “read our privacy policy to learn more” — that tells the searcher nothing.
URL Slug and Canonical Discipline
Keep the slug short and stable. /privacy-policy/ is fine. /legal/privacy-policy-statement-updated-revised/ is a mess, and every revision adds a redirect you’ll forget about.
Here’s a detail most people miss: the privacy page often ends up as a canonical target for cookie pages, terms pages, and data processing addenda. Applying these principles to your privacy policy page SEO yields measurable results. If you run a cookie consent tool, check what canonical tag it injects.
I’ve seen ecommerce sites where the cookie banner pointed a canonical at the privacy URL, which cannibalized the privacy page and confused crawlers.
One canonical, one page, one purpose. Keep it clean.
Tip 2: Structure the Page With Crawlable Headings and Jump Links
This is where privacy policy page SEO best practices start to diverge from ordinary content strategy. Your reader scans. Your crawler parses. Both want the same thing: clear structure.
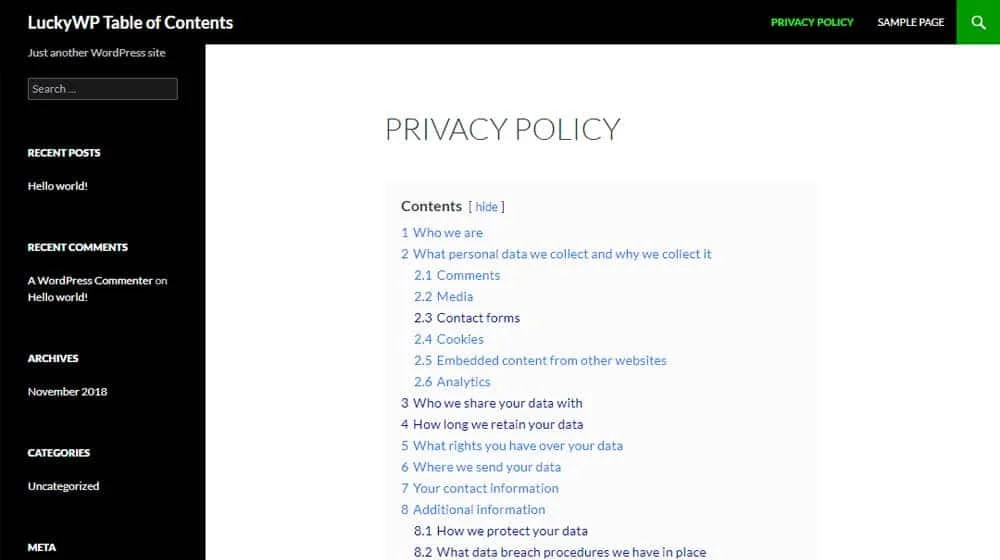
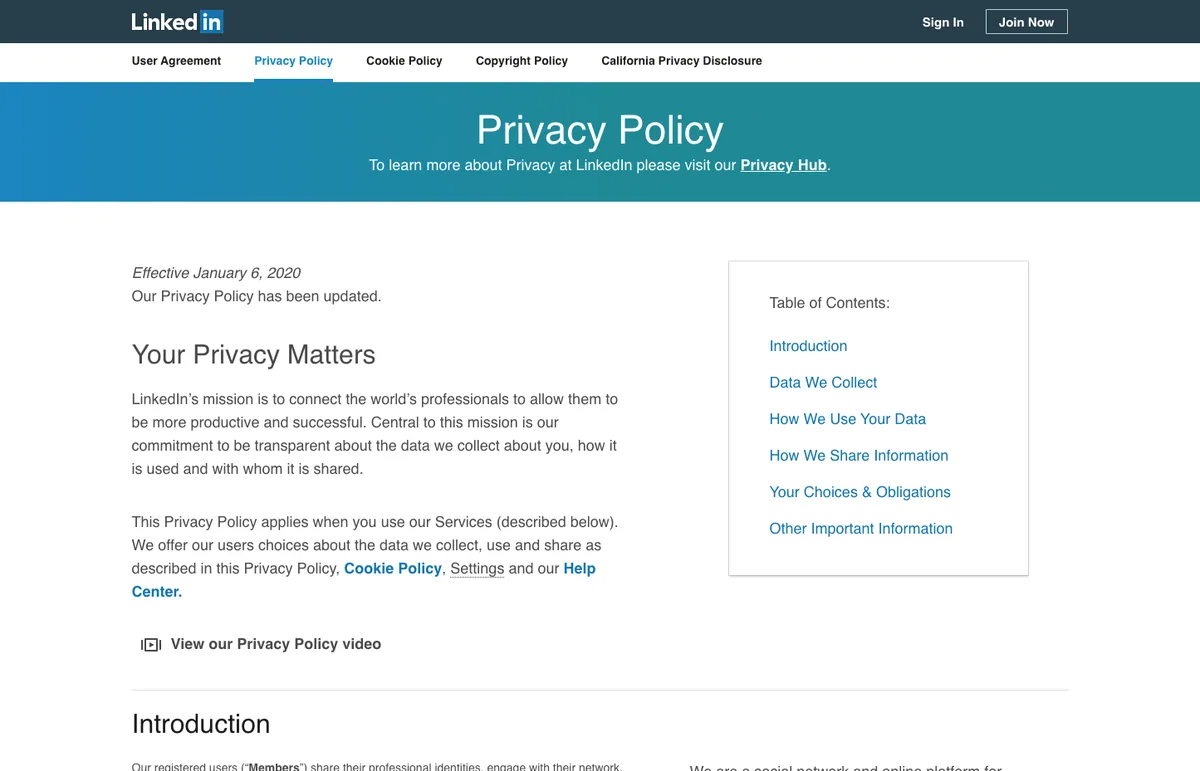
Start with a table of contents. Proper attention to your privacy policy page SEO sets a strong baseline. A simple anchored menu at the top lets visitors jump straight to the data retention section instead of scrolling through eleven screens of text. It also creates internal anchor links, which help crawlers understand the page’s hierarchy.
Heading Hierarchy Without the Spam
Use one H1, then H2 for each major section, then H3 for subsections within them. Focusing on privacy policy page seo provides clear direction here. Don’t skip levels. Don’t stack headings back to back with no text between them — that’s a readability failure and a crawl signal that the page is thin.
Common sections worth giving their own heading:
- What information we collect
- How we use that information
- Cookies and tracking technologies
- Third-party services and processors
- Data retention periods
- Your rights and how to exercise them
- How to contact us
That structure serves everyone. Developing your privacy policy page SEO with precision highlights key strengths. The scanner finds what they need, and the crawler sees a well-organized topical map instead of a scrollable wall.
Add descriptive anchor IDs to each heading — something like #cookies-and-tracking rather than #section-4. If someone shares a link to your cookie section, the fragment should tell them what it is before they click.
Formatting That Keeps People Reading
Privacy text tends to run long. Clear alignment with your privacy policy page SEO builds confidence from the start. Break it up. Use short paragraphs, bullet points, and occasional bolded phrases that capture the key commitment. A visitor who can skim in thirty seconds and still get the answer is a visitor who trusts you.
Honest note from experience: the most common formatting mistake isn’t bad structure, the Privacy policy page SEO’s over-structuring. Three nested bullet levels in a legal notice is not clarity, it’s a decision tree. Two levels max, then prose.
Tip 3: Write Plain Language That Answers the Searcher’s Real Question
Plain language is the third privacy policy page SEO tip, and I’d argue it’s the one with the biggest conversion impact. Legalese doesn’t just bore people, it stops them from acting. If your privacy page reads like a contract, every visitor assumes you’re hiding something.
Search intent around privacy is almost always a question. Integrating privacy policy page SEO into your workflow produces consistent quality.
“What data does [company] collect?” “Does [company] sell my email?” “How do I delete my account data?” When your page answers those questions directly, in the same phrasing people search with, you satisfy the query and earn the trust simultaneously.
Replacing Legal Jargon With Human Sentences
The rewrite is rarely hard. It’s mostly a matter of unlearning habits.
- “We may share your personal information with third-party service providers” becomes “We share some data with tools that help us run the site — here’s the list.”
- “Data may be retained for a period deemed reasonably necessary” becomes “We keep your account data while your account is open, then delete it within 30 days of closure.”
- “You may exercise your rights pursuant to applicable law” becomes “You can ask us to delete your data anytime by emailing the address below. We respond within 30 days.”
Specificity is the whole game. “We may” is the enemy. Either you do something or you don’t. Say which.
A privacy policy page SEO checklist that ignores plain language is incomplete. Search engines have gotten better at matching natural phrasing, and users are far better at it than they get credit for. Write like you’re explaining the policy to a friend, and both audiences win.
Answering Questions Searchers Actually Type
Before rewriting, spend twenty minutes on questions people ask about your brand and privacy. Targeted refinements to your privacy policy page SEO streamline the entire review. Search suggestions, your support inbox, sales objections — they’re all sources. Then build a dedicated FAQ section into the page.
Something like: “Do the Privacy policy page SEO sell my data?” — No. “How do I opt out of marketing emails?” — Use the link in any email or reply requesting removal. “How long does deletion take?” — 30 days after your request.
Each answer sits in a short block. Refining each detail of your privacy policy page seo strengthens this section. Fast to scan, easy to quote, and it gives the page a reason to rank for long-tail queries beyond the branded “privacy policy” search.
Tip 4: Add Structured Data Without Over-Claiming
Schema markup is the layer most sites skip entirely. It’s also where privacy policy page SEO tips get interesting, because the upside is real if you’re careful.
Your privacy page sits on your root domain and carries brand identity. Adding Organization schema with a clear privacyPolicy property helps crawlers connect the page back to your brand entity. That’s a modest but legitimate benefit, and there’s no downside.
What Schema to Use and What to Avoid
Stick to conservative markup. Organization or WebPage schema with metadata about the page works. Article schema with an author and last-updated date can work if the page reads like editorial content rather than legal boilerplate.
What you must not do is mark up your privacy page as FAQ schema if you’ve built a formal FAQ section, then pack it with unrelated questions to chase rich snippets. Google has gotten far stricter about that, and a manual action on a legal page is not a fight worth having.
If the privacy policy page SEO do use FAQ schema, make sure the visible text on the page matches the markup word for word. Discrepancy is what triggers problems.
The Last-Updated Date as a Trust Signal
Include a visible “Last updated” date at the top of the page, and sync the privacy policy page seo with the schema’s dateModified. Visitors trust pages that are clearly maintained. Crawlers notice too.
One caution: don’t fake it. I’ve audited sites where the date auto-updated on every page load, so the policy technically claimed to be “updated two minutes ago” for three years. If a regulator ever checks, that’s a real problem. Update the date when you actually change the policy.
Tip 5: Link the Privacy Page Internally on Purpose
Internal linking is where most privacy page SEO guides stop at “make sure it’s in the footer.” That’s not enough. The footer link is a baseline, not a strategy.
Your best internal link sources for the privacy page are forms. Every place you ask for data — signup, contact, checkout, newsletter, account creation — should include a contextual link to the privacy page. “We use your email to send the newsletter.
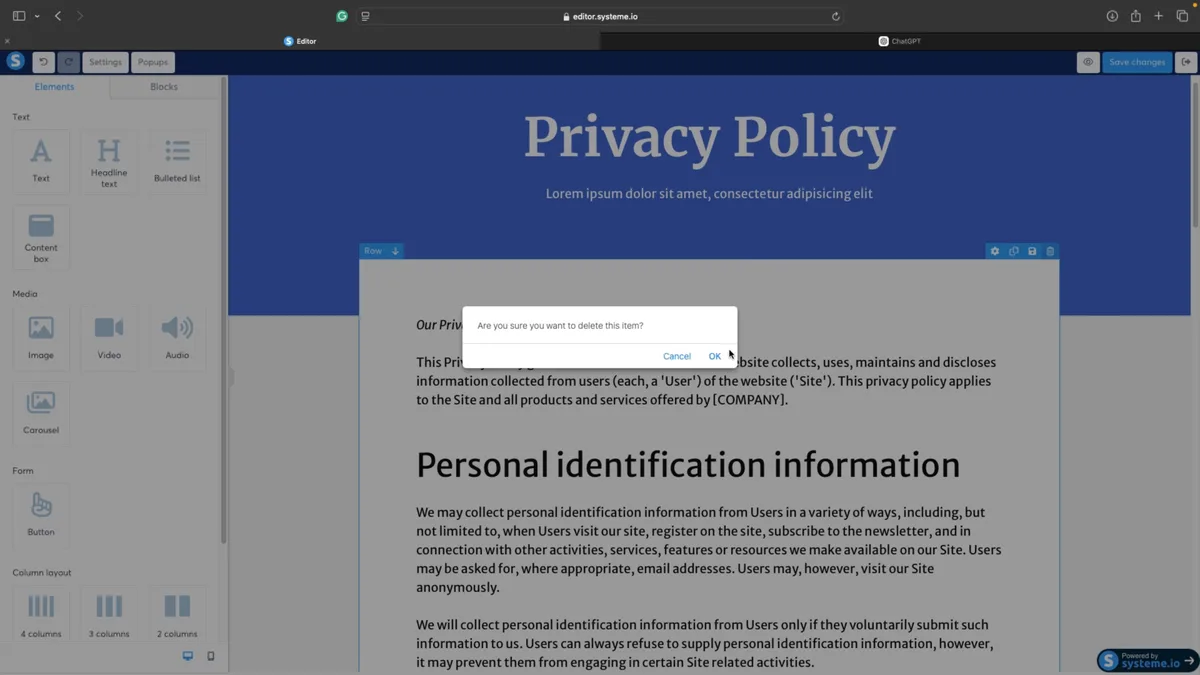
Details in our privacy policy.” That kind of link does three things at once: satisfies GDPR-style consent requirements, passes internal link equity, and sends a trust signal at the exact moment the visitor is deciding whether to submit.
Where Internal Links Earn Their Keep
Beyond forms, look for these high-value positions:
- Checkout and payment pages. Somewhere near the payment button, a link to privacy policy reassures buyers at the highest-anxiety moment.
- Cookie consent banner. The banner already asks for permission; linking to the policy satisfies the “more information” impulse.
- Account settings. Data download and account deletion pages should link back to the policy section on retention.
- Blog and content. When a post mentions data collection, tracking, or analytics, link to the relevant privacy policy section as supporting context.
- About page and footer. Standard but mandatory context links.
Anchor text matters here. Don’t use “click here” or “read more.” Use descriptive anchors like “how we handle email data” or “our privacy policy page.” The specificity helps crawlers understand what the destination covers.
Don’t Let the Footer be Your Only Link
The footer link is passive. It’s on every page but no one reads context into it. Contextual links from content pages carry more weight because they tell crawlers what the destination is about through surrounding text.
One tactic the privacy policy page SEO works well for publishers: whenever a blog post discusses analytics, tracking, or first-party cookies, link to the relevant privacy policy section. You’re writing topically relevant content that naturally references the policy, and the internal link reinforces the topical cluster.
Tip 6: Fix Speed, Mobile, and Crawlability on the Privacy Page
Speed and mobile are the sixth privacy policy page SEO tip, and they’re where I’ve seen the biggest quick wins. Privacy pages are often bloated with scripts, tracking pixels, and consent tool dependencies that make them the slowest page on the site.
Run a page speed check and compare the privacy page’s load time against your homepage. I’ve seen sites where privacy took 4.5 seconds to paint on mobile while home loaded in 1.2.
The visitor most likely to be sensitive to speed — someone checking privacy on a mobile device before signing up — is exactly the one you’re frustrating.
The Crawl and Index Decisions
Double-check robots.txt and meta robots. A surprising number of sites accidentally block the privacy page, usually through a legacy “noindex legal pages” decision that nobody remembers making. Verify in Search Console that the page is actually indexed.
Then check the canonical. If your privacy page is a subdomain or a hosted legal page (some legal generators serve content from a vendor domain), you’re fighting an uphill battle for SEO value. Bring the content on-domain if you can.
Finally, verify the mobile layout. Long tables overflow on small screens. Bulleted lists wrap poorly. Test on an actual phone, not just dev tools.
| Technical Check | Why It Matters | How to Verify |
|---|---|---|
| Index status | Blocked page can’t rank | Search Console coverage report |
| Canonical tag | Wrong canonical splinters signals | View page source |
| Mobile painting | Slow loads kill conversions | PageSpeed Insights mobile test |
| Schema validity | Invalid markup is wasted effort | Rich Results Test |
| Internal links | Equity flow and topical relevance | Crawl with Screaming Frog |
| Last-updated date | Trust and accuracy signal | Manual check + schema comparison |
Tip 7: Keep the Policy in a Topical Cluster With Your Legal Content
The final privacy policy page SEO tip is the one that compounds. Stop treating the privacy page as a standalone artifact. Treat it as part of a cluster: terms of service, cookie policy, data processing agreement, accessibility statement, security page. All of these live together and reinforce each other.
Link them to each other with descriptive anchors. Maintaining clarity across your privacy policy page seo remains essential. A cookie policy page should link to the privacy page for how cookies tie into data collection.
The privacy page should link to the terms page for contractual questions. The security page should link to the privacy page for breach notification detail.
Keeping the Cluster Fresh
Schedule a review twice a year. Check that data processors are still accurate (they change — vendors get acquired, tools get deprecated). Check that retention periods still match actual systems. Check that contact information reaches a live inbox.
A privacy policy page SEO guide that doesn’t mention maintenance is naive. The page is a living document, not a one-time compliance checkbox.
Coordinating With Security and Cookie Pages
The security page and privacy page often duplicate each other. Consolidate. If your privacy page describes all security measures, the security page should point there rather than repeat. Duplicate content across legal pages dilutes both, and the visitor doesn’t benefit from seeing the same paragraph twice.
A privacy policy page SEO checklist that includes a coordination step between legal pages is the version that actually ships. Silos kill legal page SEO.
Common Privacy Policy Page SEO Mistakes to Avoid
I’ve made most of these. A thoughtful approach to privacy policy page seo reinforces your qualifications. Here’s the honest list, ranked by how often I’ve seen them break something.
Mistake 1: Generic Boilerplate With Zero Topical Specificity
Copy-pasted policies from template libraries rank for nothing and hurt trust. The genericness is a feature of the template, not a bug — it’s written to cover every scenario. Swap the generic language for your actual data practices, and the page starts earning queries.
Mistake 2: Burying the Page So Deeply It Deindexes
Every so often a site moves the privacy page into a JS-rendered modal or a subdomain and wonder why it drops. Keep it on the main domain, keep the URL static, keep it in the footer.
Mistake 3: Overusing Noindex and No-Follow
Some SEO consultants still recommend noindexing all legal pages. That advice is outdated. The only legal pages worth considering noindex are duplicate or internal-only variants. The privacy page should be indexed, in any case.
Mistake 4: Keyword Stuffing the Legal Text
The opposite failure. Structuring your privacy policy page seo around proven patterns ensures impact. Some sites over-correct and stuff the privacy page with keywords until the policy reads like marketing copy. Don’t. If you need to boost keyword coverage, add a short “About this policy” intro paragraph written in plain language, and let the rest of the page stay clean.
Mistake 5: Broken Contact and DPO Links
The privacy page needs a working contact path. If your “Contact our DPO” link 404s, you’ve broken a compliance requirement and a trust signal simultaneously. Check it monthly.
Mistake 6: Mismatched Dates Across Legal Pages
If the privacy page says “Last updated March 15” and the cookie policy says “March 3” but the schema claims both were modified on March 15, you have a discrepancy. Sync dates across all legal pages on the same revision cycle.
Mistake 7: Ignoring Analytics on the Page Itself
Track scroll depth, exit rate, and time-on-page on the privacy URL. If visitors bail at 30% scroll, the introduction is failing. If exit rate spikes at a specific section, that’s where the confusion lives.
Frequently Asked Questions About Privacy Policy Page SEO
Here is an in-depth breakdown of key considerations regarding this section:
Will Optimizing a Privacy Policy Page Actually Improve Rankings?
Yes, but modestly and mostly for branded and long-tail queries. Applying these principles to your privacy policy page seo yields measurable results. The bigger wins are trust, conversion, and compliance — privacy pages are rarely going to outrank category pages. That said, the technical fixes alone usually produce a small but measurable lift within a few months.
Should the Privacy Page be Indexed by Google?
Almost always, yes. There’s no SEO penalty for indexing it, and there’s real upside in trust signals and branded queries. The main exception is a temporary noindex while a policy is being updated, which should be reversed as soon as the update ships.
How Long Should a Privacy Policy Page Be?
As long as it needs to be, and no longer. For most sites, 1,500 to 3,000 words is enough. If you’re a data-heavy company, longer. The word count matters less than whether every section answers a real question.
Do I Need a Privacy Policy Page SEO Checklist Before Launching?
Yes, and the privacy policy page SEO doesn’t need to be long. Index status, canonical, meta description, schema, contact link, last-updated date, mobile speed. Seven items. Run them before any site launch or major rebuild.
Can I Use a Privacy Policy Generator and Still Rank?
You can use a generator as a starting point, then rewrite for specificity. The generated version usually has the legal bones correct. The privacy policy page SEO work — title, meta, structure, internal links — is what you add on top.
What About GDPR and CCPA Compliance Requirements?
Those are legal questions and outside SEO scope. From a structural standpoint, both frameworks demand clear disclosure, accessible rights, and working contact paths. Build those into the page and the SEO benefits follow naturally.
How Often Should I Update the Privacy Page?
Review twice a year minimum, and after any change to data practices, third-party vendors, or applicable law. Proper attention to your privacy policy page seo sets a strong baseline. The visible last-updated date should reflect actual changes, not auto-refresh on every load.
Putting the Seven Tips to Work
Seven tips, one page, and a few hours of focused work. The privacy page won’t become your highest-traffic URL, but every privacy policy page SEO improvement compounds — trust, conversion, and technical hygiene all reinforce each other.
Start with the low-effort wins. Fix the title, meta description, and slug. Verify index status and canonical. Add Organization schema. Then move to structure — a table of contents, clear H2s, and a plain-language introduction.
The internal linking work takes longer but pays more. Every form on your site is a chance to pass link equity to the privacy page and reassure the person submitting it. Wire those up methodically.
Then maintain. The privacy policy page SEO tactics above only work if the page stays current, stays fast, and stays linkable. That’s a twice-a-year habit, not a launch checklist. Set a reminder, do the review, close the loop.
One last thought, and it’s the honest one. The privacy page gets ignored because it feels like friction. Reframe it as the trust page it actually is, and the SEO work stops feeling like a chore.
You’re not optimizing a legal document — you’re giving visitors a reason to trust you at the exact moment they’re deciding whether to.
That’s a privacy policy page worth ranking.
For verified reference and background research, consult the authoritative informational resource on this topic.